Cybersecurity Analyst ATS Resume Template
Jake's Single-Column Format
A single-column Cybersecurity Analyst sample in the Jake's Resume layout, with X-Y-Z bullets and keywords to compare against a job description.
Nearest BLS wage, checked October 6, 2026: Information security analysts, May 2025 median pay $129,180.
Occupational Outlook Handbook. The nearest Handbook occupation for a cybersecurity analyst posting is information security analysts, SOC 15-1212. A narrow tool-specific analyst role can differ from that median. This is not a FairCV survey.
Interactive Template Preview
Jake's Resume-Inspired Layout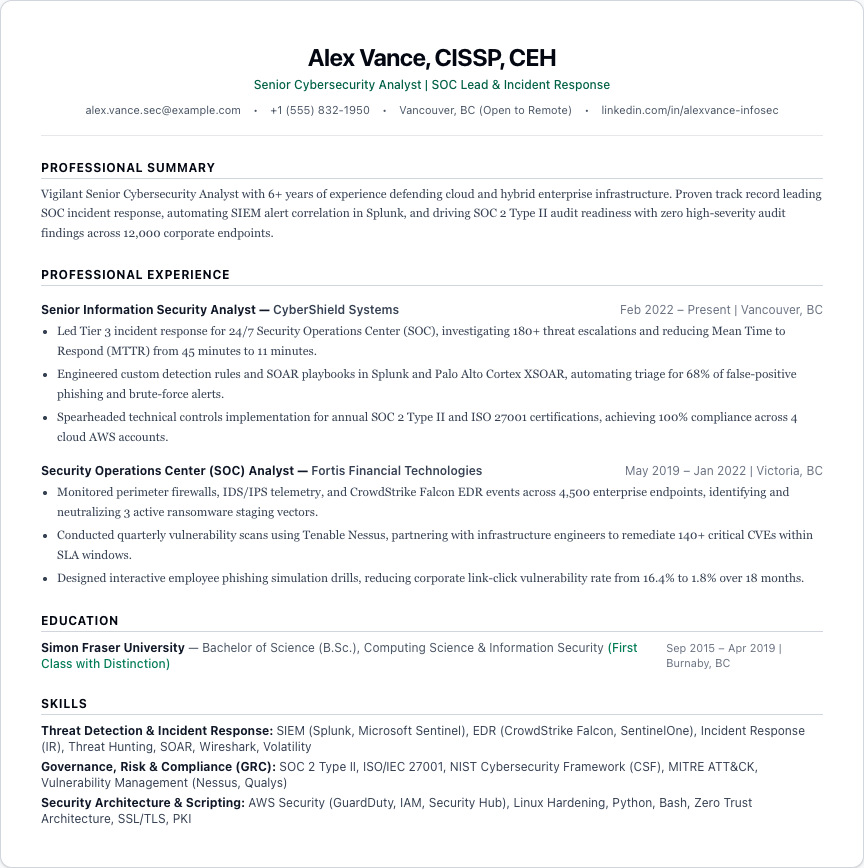
Alex Vance, CISSP, CEH
Senior Cybersecurity Analyst | SOC Lead & Incident Response
Professional Summary
Vigilant Senior Cybersecurity Analyst with 6+ years of experience defending cloud and hybrid enterprise infrastructure. Proven track record leading SOC incident response, automating SIEM alert correlation in Splunk, and driving SOC 2 Type II audit readiness with zero high-severity audit findings across 12,000 corporate endpoints.
Professional Experience
- Led Tier 3 incident response for 24/7 Security Operations Center (SOC), investigating 180+ threat escalations and reducing Mean Time to Respond (MTTR) from 45 minutes to 11 minutes.
- Engineered custom detection rules and SOAR playbooks in Splunk and Palo Alto Cortex XSOAR, automating triage for 68% of false-positive phishing and brute-force alerts.
- Spearheaded technical controls implementation for annual SOC 2 Type II and ISO 27001 certifications, achieving 100% compliance across 4 cloud AWS accounts.
- Monitored perimeter firewalls, IDS/IPS telemetry, and CrowdStrike Falcon EDR events across 4,500 enterprise endpoints, identifying and neutralizing 3 active ransomware staging vectors.
- Conducted quarterly vulnerability scans using Tenable Nessus, partnering with infrastructure engineers to remediate 140+ critical CVEs within SLA windows.
- Designed interactive employee phishing simulation drills, reducing corporate link-click vulnerability rate from 16.4% to 1.8% over 18 months.
Education
Skills
Pre-populate your work history and export unwatermarked PDFs for $4 flat. No monthly subscriptions.
Ten terms from the Cybersecurity Analyst example
These ten terms were chosen from the example posting on this page on October 6, 2026. The list is a starting point for that sample. It is not a study of applicant tracking systems, and it is not a ranking of what recruiters scan for. Paste a real posting into the matcher on the homepage to see which terms already appear on your resume.
Open the builder and paste a real posting into the keyword matcher. The sample list above is only the starting point.
Example job description
Original example written by FairCV on October 6, 2026. It is not an employer job ad.
Cybersecurity analyst, security operations
Portside Mutual is hiring a cybersecurity analyst for the security operations queue. The tools are a SIEM (Splunk, Microsoft Sentinel), incident response (IR) runbooks, and threat hunting and detection on the alerts that survive the first filter. Endpoints report through an EDR (CrowdStrike Falcon).
The control set follows SOC 2 Type II and ISO 27001 evidence requests, mapped to the NIST Cybersecurity Framework. Vulnerability management (Nessus) is a weekly pass. New detections need MITRE ATT&CK mapping. Python and Bash automation is how the team retires a repeating ticket. Zero trust architecture is the standard the network team is rolling out, and this role reviews the exceptions.
Wage note from the Handbook
The Handbook lists median pay of $129,180 in May 2025. The same page lists the 10th percentile at $75,090 and the 90th percentile at $199,850.
Source, checked October 6, 2026: Information security analysts in the Occupational Outlook Handbook.
Google X-Y-Z Bullet Point Breakdown
How Google hiring executives recommend structuring resume bullets: "Accomplished [X] as measured by [Y], by doing [Z]".
Why this line is specific: MTTR is the benchmark metric every Chief Information Security Officer (CISO) cares about.
Why this line is specific: Shows automation and engineering acumen, preventing security analyst burnout.
Why this line is specific: Compliance is enterprise currency; proving audit-readiness makes hiring you risk-free.
⚠️Common Mistakes for Cybersecurity Analysts
- ×Failing to list specific SIEM (Splunk, QRadar) or EDR (CrowdStrike) vendor tools.
- ×Speaking in vague terms ("Helped keep network safe") with zero incident metrics.
- ×Leaving certifications like CISSP, CEH, or Security+ scattered throughout the text.
✓Hiring Manager Recommendations
- ✓Highlight industry certifications (CISSP, Security+, CEH, CISM) immediately in your headline.
- ✓Reference the MITRE ATT&CK framework when describing detection rules.
- ✓Quantify the size of the infrastructure you defended (number of endpoints, cloud accounts, users).
Ready to Export Your Cybersecurity Analyst Resume?
Start editing immediately in our clean visual builder. No monthly recurring traps, no surprise credit card bills. $4 flat single export or $14 for 30 days.